RegORegO
Pricing

Move from Periodic Compliance to
Continuous Assurance

See how RegO connects controls, evidence, assessments and remediation in one continuously updated platform.

OSCAL Platform

  • OSCAL Flow
  • Catalog & SSP
  • Continuous Compliance
  • Drift Detection
  • Assessment Execution

Insights & AI

  • Live Insights
  • Control Effectiveness
  • Executive Dashboards
  • AI Capabilities

By Solution

  • Operating Modes
  • Challenges Solved
  • Framework Coverage
  • Connectors

By Industry

  • Banking & Financial Services
  • Government & Public Sector
  • Insurance
  • Healthcare

Learn

  • Use Cases
  • Whitepapers
  • Blog

Product

  • Resource Library
  • Product Roadmap

Company

  • About Us
  • Why RegO
  • Leadership

More

  • Pricing
RegORegO

RegO is an OSCAL-native continuous compliance platform that unifies governance, risk, controls, evidence and assessments into one intelligent ecosystem.

© 2026 RegO · All rights reserved.

How Organizations put RegO to work

From continuous audit readiness to policy-as-code enforcement. Real ways compliance, security and platform teams turn RegO into an everyday operating advantage.
Continuous Monitoring

Many organizations assess compliance only during audit cycles, creating blind spots between assessments and making audit preparation reactive. RegO helps teams maintain an ongoing view of control status, evidence availability, findings, remediation progress, and compliance trends.

Read more

Audit Readiness

Audit preparation often becomes stressful because evidence is scattered, ownership is unclear, and control status is manually tracked. It isn't enough to say a control is satisfied; teams must show how that conclusion was reached and what evidence supports it. RegO connects controls, assessment responses, evidence, findings, remediation actions, and reports in a single platform, establishing a clear line of traceability across the full compliance lifecycle, from framework control, through SSP, assessment plan, control response, and evidence, to finding, POA&M item, milestone, and final report.

Read more

SSP & Assessments

A System Security Plan should clearly define the system boundary, components, ownership, control implementation, and compliance scope. RegO enables teams to create and maintain SSPs as part of the compliance lifecycle, ensuring assessments are grounded in a clear system context. From there, RegO supports the full assessment workflow, from planning to execution, review, and reporting, even when multiple controls, assessors, reviewers, and evidence owners are involved.

Read more

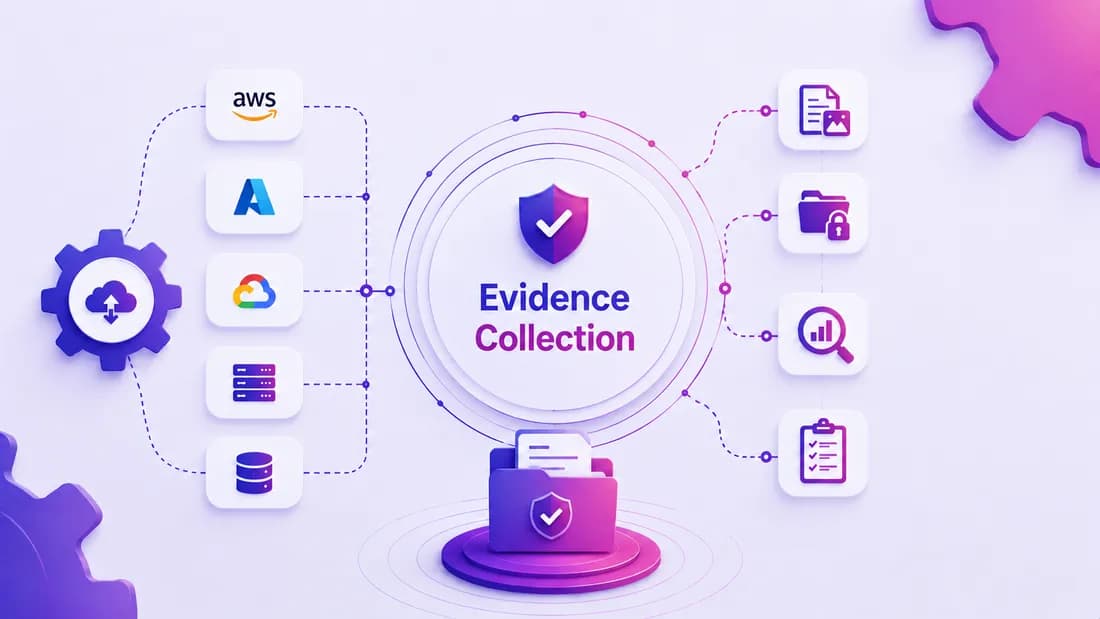
Evidence Collection

Not all controls can be tested the same way. Some require management attestation, some require supporting evidence, and some can be validated technically. Evidence itself is often collected through emails, shared folders, and ad-hoc documents, making it difficult to verify completeness. RegO supports three assessment methods within one platform, and provides a structured way to collect, review, and link evidence to control assessments:

Read more

Remediation Tracking

Assessment results are only useful when gaps are clearly identified, prioritized, assigned, and tracked. RegO converts not-satisfied controls and technical failures into findings, and helps manage the resulting Plan of Action and Milestones (POA&M), including remediation plans, target dates, ownership, and closure status.

Read more

Compliance Reporting

Leadership needs more than a raw control list; they need to know whether the organization is audit-ready, where the key risks are, and what needs attention first. Auditors and regulators need structured, submission-ready reports that bring together assessment results, evidence status, findings, and remediation history. RegO generates one set of structured reports that serves both needs.

Read more

Who Uses RegO

Teams across the organization rely on RegO to streamline compliance operations, reduce manual effort and achieve continuous assurance. RegO empowers every role to collaborate, act with confidence and stay audit-ready every day.

Collaborate

Work together across teams with shared data and unified workflows.

Gain Visibility

Get real-time insights into controls, risks and compliance posture.

Automate

Automate evidence collection, assessments and reporting.

Stay Audit-Ready

Maintain accurate, traceable evidence and be ready for any audit.

Compliance Teams

Manage controls, assessments, policies, evidence collection, reporting and overall compliance posture.

01

Internal Audit Teams

Review control status, evidence, findings and audit trails with full traceability.

02

Risk Teams

Track risks, identify gaps, monitor remediation plans and produce governance reports.

03

Security Teams

Validate technical controls, monitor configurations and ensure evidence-backed security compliance.

04

Technology Owners

Respond to assessments, provide system evidence and remediate findings efficiently.

05

Leadership Teams

View real-time compliance posture, risk exposure, trends and remediation priorities.

06